Published: October 31, 2026 | Category: AI News
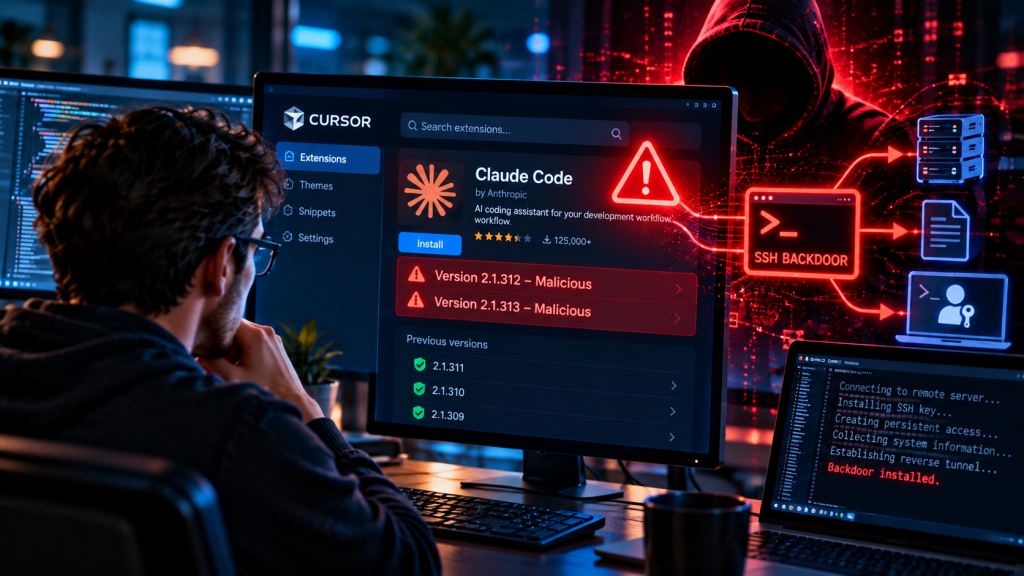
A maliciously modified version of the Claude Code extension was distributed through Cursor’s extension marketplace on October 29, 2026, exposing developers to a potential persistent SSH backdoor.
Cursor confirmed that two affected versions, 2.1.312 and 2.1.313, were available through its marketplace for approximately 11 hours. The malicious packages were not developed by Anthropic, the company behind Claude and Claude Code.
Microsoft Threat Intelligence subsequently analyzed the injected code and confirmed that it attempted to establish unauthorized remote access, collect system information, and create mechanisms that could survive after the extension was removed.
Cursor has removed the affected packages and worked with the hosting provider to take the attacker’s server offline. However, users who installed the compromised versions may still need to inspect and clean their computers.
What Happened to the Claude Code Extension?
On October 29, 2026, attackers managed to distribute modified versions of the Claude Code extension through the Cursor VS Code Extension Marketplace.
According to Cursor’s official security notice, the affected packages were available between approximately 2:27 a.m. and 1:35 p.m. Pacific Daylight Time.
The malicious versions were identified as:
Anthropic.claude-codeversion2.1.312Anthropic.claude-codeversion2.1.313
The affected packages targeted macOS and Windows users downloading or updating the extension through Cursor’s marketplace.
The distinction between distribution channels is important.
Microsoft confirmed that the malicious packages were not distributed through the Microsoft Visual Studio Marketplace or the official Claude Code npm package.
Anthropic also confirmed to Microsoft that its systems had not been compromised and that it did not create the malicious packages.
The available evidence points to a compromise involving the Cursor extension distribution channel, rather than a confirmed breach of Anthropic’s infrastructure.
How Did the Malicious Extension Work?
The attackers inserted JavaScript into the extension package.
According to Microsoft’s technical investigation, the injected code executed when the extension loaded, before its normal functionality initialized.
The code attempted several actions that could provide an attacker with access to a developer’s computer.
1. Collecting System Information
The malicious code gathered information about the affected computer, including:
- Hostname and username
- Operating system and architecture
- Home directory and working directory
- Configured Git email address
- Names of potentially sensitive environment variables
Microsoft found that the initial collection of environment-variable names did not, by itself, demonstrate theft of the secret values stored in those variables.
However, the information could help an attacker understand the system and identify potential targets for further activity.
2. Installing an Unauthorized SSH Key
The extension attempted to modify the computer’s SSH configuration.
SSH, or Secure Shell, is a technology commonly used by developers and system administrators to connect securely to remote computers.
The malicious code attempted to add an attacker-controlled public key to an SSH authorization file.
This could allow someone possessing the corresponding private key to authenticate if the computer’s SSH server was accessible and correctly configured for the attack.
3. Creating a Reverse SSH Tunnel
The malware also attempted to establish an outbound connection to an attacker-controlled server.
This technique, known as reverse SSH tunneling, can potentially provide a path back into a computer even when ordinary inbound network access is restricted.
However, an attempted connection does not mean that the attacker successfully accessed every affected machine.
Cursor reported that errors in the malicious code and administrator-permission requirements prevented the intended SSH access on most macOS and Windows systems.
4. Attempting to Maintain Persistent Access
One of the most concerning aspects of the incident was the attempt to maintain access after the original extension was removed.
The injected code could create startup scripts and other files outside the extension’s installation directory.
On macOS, it attempted to use a LaunchAgent.
On Windows, it attempted to create a scheduled task, with an additional startup-script fallback.
These mechanisms were intended to restart the malicious connection automatically.
This means uninstalling or updating the extension alone may not remove every malicious component.
Which Claude Code Users Were Affected?
The confirmed distribution incident involved specific versions of the Claude Code extension obtained through Cursor’s extension marketplace.
| Installation source | Reported status |
|---|---|
| Cursor Marketplace, malicious builds of 2.1.312 and 2.1.313 | Affected |
| Microsoft Visual Studio Marketplace | No evidence of affected distribution |
| Official Claude Code npm package | Not affected by this incident |
| Other Claude Code extension versions | No evidence of compromise reported by Cursor |
A version number alone is not enough to establish compromise.
For example, version 2.1.312 also existed as a legitimate release through other distribution channels.
Users need to consider where the extension was obtained and whether its files match the malicious indicators published by Cursor.
How to Check Whether Your Computer Is Affected
If you installed or updated Claude Code through Cursor’s marketplace on October 29, 2026, particularly during the identified exposure window, review your installation.
Step 1: Check the Installed Extension
Open Cursor and inspect the installed Claude Code extension.
Look for versions 2.1.312 or 2.1.313.
If you installed either version from Cursor’s marketplace during the affected period, follow the official security guidance.
Do not assume that an extension is safe simply because it appears to work normally.
Step 2: Check for the Unauthorized SSH Key
Cursor identified an attacker-controlled SSH key containing the marker:
svc-telemetry
On macOS, users can inspect their SSH authorized keys file at:
~/.ssh/authorized_keys
On Windows, relevant locations include:
%USERPROFILE%\.ssh\authorized_keys
and, where applicable:
C:\ProgramData\ssh\administrators_authorized_keys
The presence of the confirmed malicious key is a strong indication that the injected code executed.
However, the absence of that marker does not necessarily rule out every form of exposure. Extension installation records, network activity, and other artifacts may also need investigation.
Step 3: Use Cursor’s Official Security Checks
Cursor has published platform-specific validation and remediation scripts in its official security notice.
Users should obtain these tools directly from the original security advisory, review the instructions, and follow the stated operating-system requirements.
Avoid downloading unofficial cleanup utilities from third-party websites.
Step 4: Remove Confirmed Malicious Artifacts
Affected systems may require removal of:
- The compromised extension package
- Unauthorized SSH keys
- Malicious startup scripts
- Persistence mechanisms
- Suspicious SSH tunnel processes
Because some components may remain outside the extension directory, removing the extension is not necessarily sufficient.
For business computers or machines containing sensitive credentials, involve the organization’s security or IT team before making changes that could destroy forensic evidence.
Step 5: Review Credentials and Sessions
If investigation indicates that an attacker accessed the computer, or the device can no longer be trusted, review potentially exposed credentials.
Depending on the findings, this may involve rotating API keys, changing passwords, revoking active sessions, and rebuilding the affected machine.
These actions should be performed from a trusted device.
What Has Cursor Done About the Incident?
Cursor says it removed the malicious packages after discovering the problem and blocked further distribution.
The company also temporarily shut down its extension marketplace, audited other extensions, rotated relevant keys, and rebuilt the marketplace infrastructure.
Cursor worked with the hosting provider to disable the attacker’s server.
This disrupted the infrastructure used by the malicious extension.
However, disabling the external server does not automatically remove unauthorized SSH keys or persistence files that may already exist on users’ computers.
That is why Cursor continues to recommend remediation for potentially affected systems.
Was Anthropic or Claude Itself Hacked?
Based on the information published by Cursor and Microsoft, there is no confirmed evidence that Anthropic’s systems were compromised in this incident.
The malicious packages were distributed through Cursor’s marketplace and were not developed by Anthropic.
This is an important distinction.
The incident does not establish that Claude’s underlying AI models were compromised or that ordinary Claude conversations were exposed.
Instead, it demonstrates a security risk associated with software extensions and the systems used to distribute them.
Claude Code remains a dedicated AI coding tool developed by Anthropic.
For a broader look at Anthropic’s AI ecosystem and how it compares with OpenAI’s offerings, read our ChatGPT vs Claude comparison.
Why This Incident Matters for AI Coding Tools
AI coding assistants have become increasingly integrated into software development workflows.
These tools can help developers understand repositories, modify files, generate code, and automate repetitive tasks.
However, extensions running inside development environments may also have significant access to local systems.
A malicious extension can potentially interact with source code, local files, environment settings, and development credentials.
This makes extension marketplaces an attractive target for supply-chain attacks.
The Claude Code incident illustrates three important security lessons.
Extension Distribution Is Part of the Security Chain
Even when a software developer is trustworthy, the systems distributing its software must also be protected.
A compromised distribution channel can expose users to malicious software that appears to come from a legitimate publisher.
Automatic Updates Can Introduce Risk
Automatic updates are valuable for receiving security fixes, but a malicious update can also reach users quickly if an extension distribution system is compromised.
Organizations managing sensitive development environments may benefit from approved-extension policies and controlled update procedures.
Removing Malicious Software May Not Be Enough
When malware creates additional files, credentials, or startup mechanisms, uninstalling the original package may leave the system exposed.
Effective remediation requires checking for the full set of malicious artifacts.
How Can Developers Reduce Similar Risks?
Developers using Claude Code, Cursor, or other AI coding tools can reduce their exposure by adopting several security practices.
Install extensions from trusted distribution channels. Verify the publisher and source before installing new development tools.
Review unexpected updates. Pay attention to unusual version changes, installation prompts, or unexpected permission requests.
Limit unnecessary privileges. Avoid running development applications with administrator permissions unless required.
Protect development credentials. Use appropriate secret-management tools and avoid granting extensions more access than necessary.
Follow official security advisories. When an incident occurs, rely on verified instructions from the affected software provider and trusted security researchers.
No single measure eliminates supply-chain risk, but these practices can reduce the potential impact of malicious extensions.
Frequently Asked Questions
Is Claude Code safe to use after the Cursor extension incident?
The incident involved maliciously modified extension packages distributed through Cursor’s marketplace. Microsoft reported no evidence that the official Claude Code npm package or Microsoft Visual Studio Marketplace distribution was affected.
Users should still follow official security guidance and verify their installations.
Which Claude Code versions were malicious?
Cursor identified malicious builds labeled 2.1.312 and 2.1.313 for macOS and Windows in its marketplace. The version number alone does not establish whether an installation was malicious.
Can uninstalling Claude Code remove the backdoor?
Not necessarily. The malicious code attempted to create persistence mechanisms outside the extension installation directory. Affected users should follow Cursor’s complete remediation instructions.
Were Claude conversations or Anthropic accounts compromised?
The published findings do not establish a breach of Anthropic’s systems or ordinary Claude conversations. The confirmed incident concerned malicious extension packages distributed through Cursor.
Is the attacker’s server still active?
Cursor reported that it worked with the hosting provider to take the attacker’s server offline. Local malicious artifacts may still require removal.
Final Thoughts
The October 2026 Claude Code extension incident highlights an important risk in the growing ecosystem of AI-powered development tools.
Attackers distributed maliciously modified extension packages through Cursor’s marketplace, attempting to install a persistent SSH backdoor on developers’ computers.
Cursor removed the packages and disabled the attacker’s infrastructure, while Microsoft published a detailed technical analysis of the injected code.
The available evidence does not indicate that Anthropic’s systems were compromised.
For developers, the most important action is to verify whether they installed an affected package and follow the official remediation guidance when necessary.
The broader lesson is that securing AI development tools requires attention not only to the AI models themselves, but also to the extensions, marketplaces, permissions, and software supply chains surrounding them.
Original Sources
Primary source: Cursor — Security Notice: Malicious Claude Code Extension. Published October 29, 2026; updated October 30, 2026.
Technical investigation: Microsoft Security Blog — Inside a Malicious Claude Code-Branded Extension and Its Persistent SSH Backdoor. Published October 30, 2026.
This article is based on the official incident disclosure and Microsoft’s independent technical analysis. Information is current as of October 31, 2026.